Blog
Your AI Account Is Now Worth Stealing
Google's incident responders say criminals are hijacking cloud AI access and reselling it, leaving victims with bills above $100,000 in a single day. How the scheme works and how to lock your accounts down.
On Monday, Google's Mandiant incident response team published a warning with an ugly shape to it: criminals are breaking into company cloud accounts, switching on the AI services, and burning through other people's money. In the incidents Google investigated this year, fraudulent charges topped $100,000 in a single day, and at some organizations reached $1 million before access was cut off. The tactic is common enough now that it has a name: LLMjacking.
The way in is rarely exotic. Google's report describes stolen or exposed credentials: service account keys, GitHub personal access tokens, active session tokens. In one case, an attacker group used a misconfigured service account key to get into a cloud instance, then granted itself access to an AI API. In another, a fake application portal tricked users into pasting their live session token, letting the attacker skip the password and the second factor entirely. Models that people run themselves, left open to the public internet with no password, get scooped up the same way.
The stolen access does not stay with the thief. Google describes a supply chain: one crew breaks in, and a second crew runs what Google calls an LLM Mixer, a routing gateway that pools stolen access and resells it to anyone who wants cheap AI. One reseller Google tracked, called Jet Night, pushed more than 500,000 API calls through stolen keys in under eight hours and sold an unlimited plan for about $60 a month, far below the $100 to $250 that kind of access typically costs. The service had public outages on its Telegram channel, likely every time a victim discovered the theft and revoked a key. In a separate case CrowdStrike documented in August, a single thief fired off roughly 200,000 requests in two minutes.
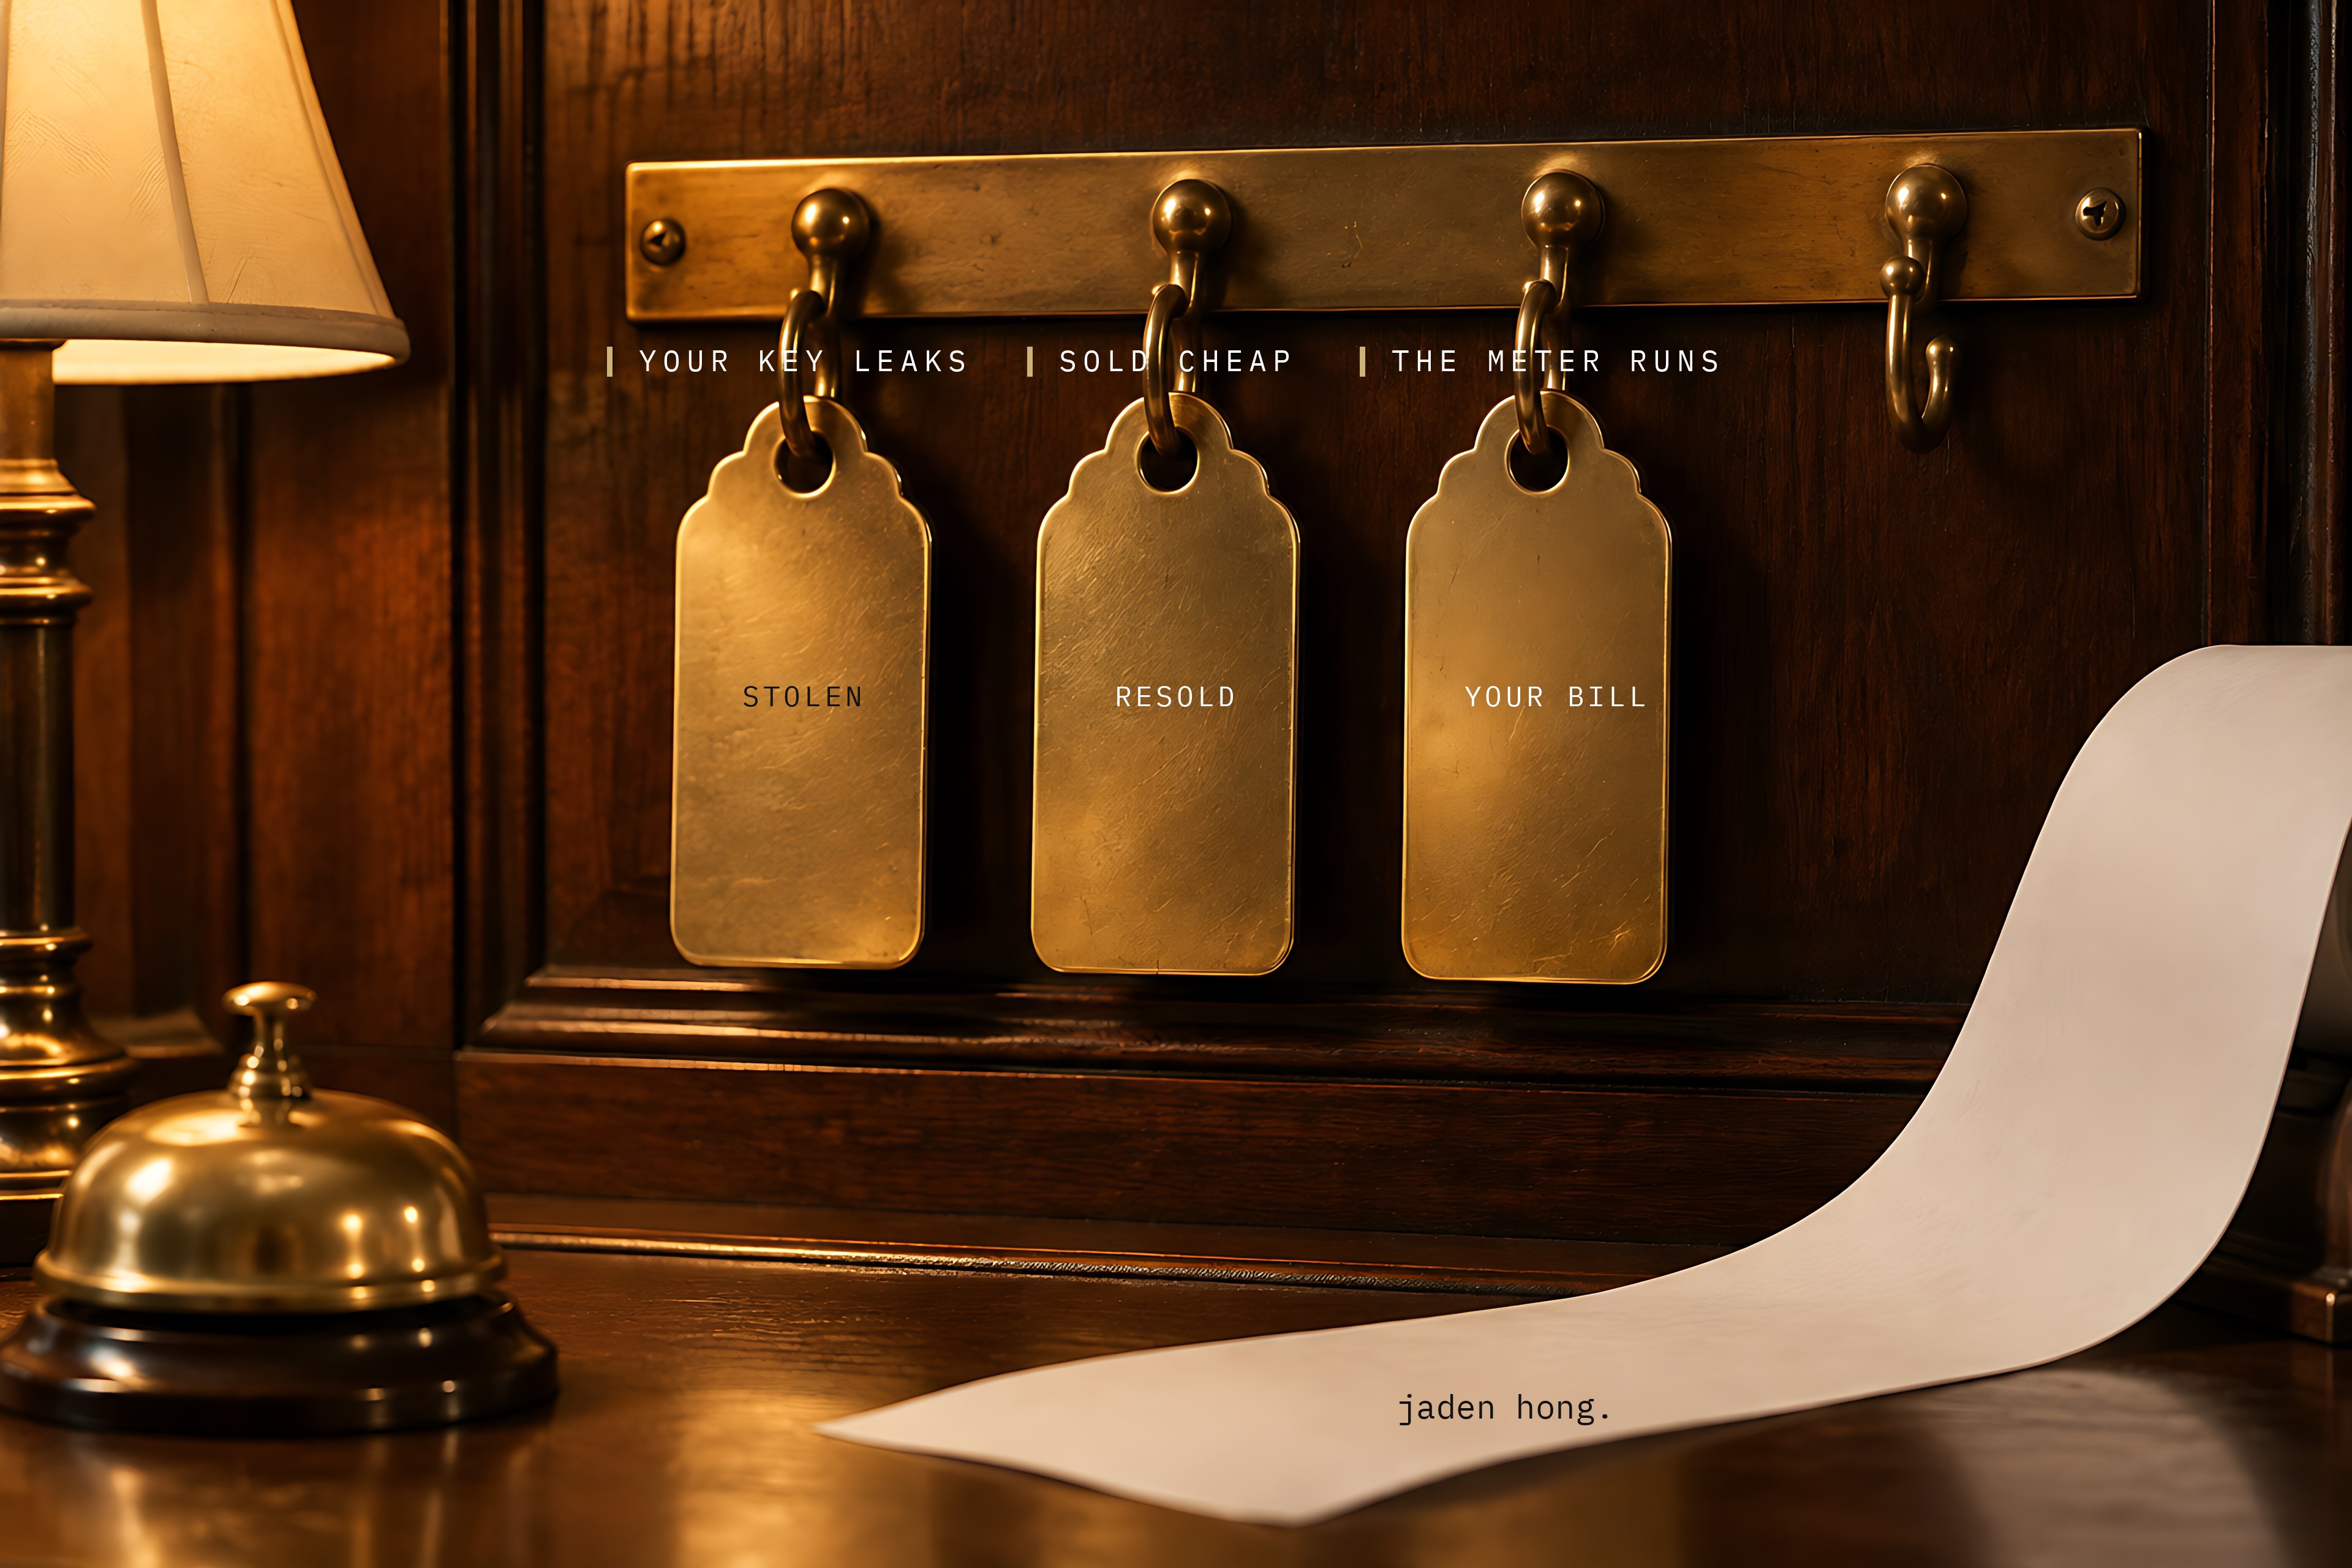
How LLMjacking pays: stolen keys are pooled by resellers and sold as cheap unlimited plans, while the usage bill lands on the key's owner. Google reports single day charges above $100,000 in individual incidents.
This matters on both sides of the transaction. As an owner: any AI key or cloud login your business holds is now a target, and the meter runs fast once it leaks. As a buyer: an unlimited AI plan priced far below the market is a red flag. You may be renting a stolen key, and it will stop working without warning the day the victim finds out.
Google's full guidance is written for security teams, but the core of it fits on an index card:
Turn on enforced spend limits where your provider offers them, and budget alerts everywhere. Check how each provider actually behaves: some limits are hard stops, others only warn or kick in late, and an alert by itself never stops the meter. Either way the bill is the alarm, so make sure it reaches you.
Put quotas on expensive models, so a stolen key cannot call the top tier.
Use a separate key for each tool, with the narrowest permissions it can work with, so one leak does not open everything.
Keep keys out of code, and turn on secret scanning if you use GitHub.
Use phishing resistant MFA on cloud consoles and developer accounts.
Watch your logs for tiny test calls. Attackers validate stolen keys with one token pings before the flood.
What it means for operators (Jaden's take)
Treat your AI keys like card numbers, because that is what they have become. My read: most small businesses will never meet the crews in Google's report, but the defense that matters costs almost nothing. This week, turn on whatever spend limits and budget alerts your AI providers offer, check whether those limits are hard stops or just warnings, and make a list of where your keys actually live. And if a service offers unlimited frontier AI at a price that makes no sense, walk away. A price that far below the market is a warning sign, not a bargain: access that cheap has to come from somewhere, and if it does turn out to be stolen, it stops working the day the real owner finds out.
Read next
Blog
One Line in robots.txt Will Soon Tell Major AI Companies: Don't Train Here
Google, Microsoft, OpenAI and Anthropic have agreed to honor a single AI training opt-out in robots.txt. Here is what the shared signal does, what it does not do, and when it actually arrives.
Blog
A Frontier AI Model Is Now a Download. That Changes Your Leverage.
Mistral just released its one-trillion-parameter flagship as open weights. Most owners will still rent AI - but the option to own it reprices everything.
Blog
AI Phone Agents for Restaurants: What They Cost Before the Holiday Rush
Four AI phone agents built for restaurants, compared on price and fit, plus a simple formula to see if one pays for itself.